Transform #24 Article
Built It, Own It?
Agencies and the Websites They Leave Behind
Opinion 4 min read
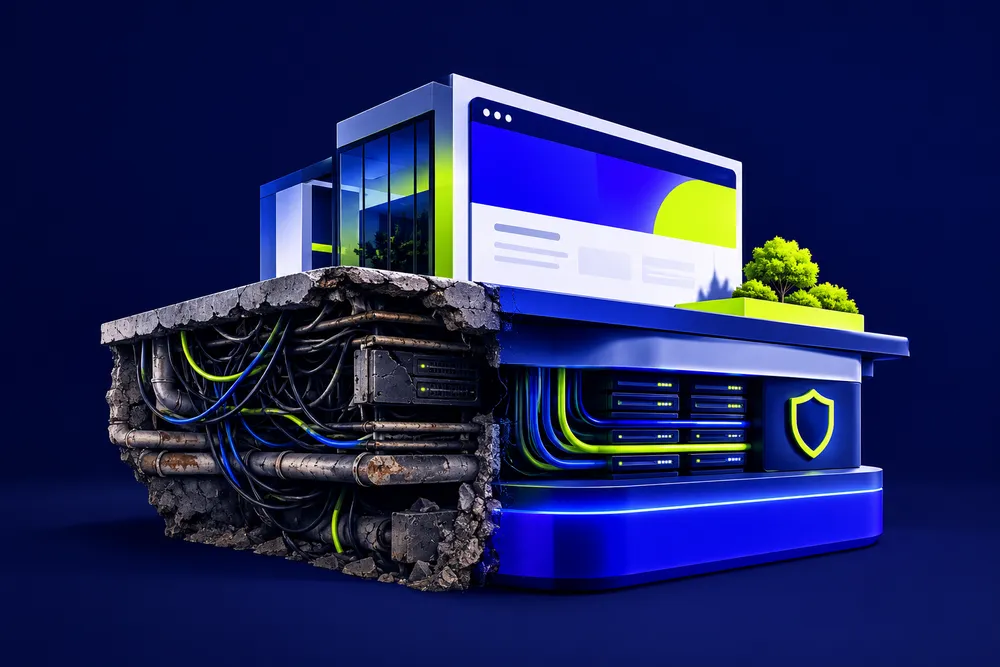
A flaw in the foundations
When a security hole opens in a website an agency built five years ago, whose problem is it? Earlier this month (October) that stopped being a theoretical question.
On 21 October 2026, PHP shipped emergency fixes for two critical flaws in its core engine, known together as PHP2Shell (CVE-2026-109618 and CVE-2026-109619). Both are rated 9.2 out of 10. They affect PHP 5.4 through 8.5.11, which covers most WordPress, Drupal and Joomla builds, plus a long tail of custom PHP sites.
The sting is in the detail. Official patches exist only for PHP 8.2 and above. Sites on 8.1, 8.0, 7.x or 5.x get nothing. Those are the older builds, and they are overwhelmingly agency builds: launched, handed over, and left to run.
The handover myth
Agencies treat launch as the finish line. Clients treat it as the start. That gap is where risk lives.
In 30+ years in agency land I've signed off hundreds of launches. The site goes live, the invoice goes out, the team moves to the next brief. Maybe there's a retainer. Often there isn't. The client walks away believing their website is "done", the same way a building is done.
But a website is closer to a car than a building. It sits on an engine, a language runtime, a database, dependencies and a host, each with its own life cycle. Every one of those parts ages from the day of launch. A site nobody touches is not stable. It is decaying quietly, every day.
Everyone assumes someone else has it
Ask most agencies a simple question: who is checking the sites you built in 2019? The honest answer, more often than not, is nobody in particular.
Party | What they assume | What tends to be true |
|---|---|---|
Client | The agency or host keeps it safe | No one is contracted to patch the runtime |
Agency | The client owns it after handover | The client still calls the agency when it breaks |
Host | Customers manage their own PHP version | Old versions keep running unless someone moves them |
Original developer | Long gone to another job | The knowledge left with them |
Legally, the contract may say the client owns the risk. Commercially and reputationally, it lands on the agency. When a client's site starts serving malware, the first call goes to the people whose name sits in the footer.
Why it keeps happening
None of this is negligence. It is the business model doing what it was built to do.
Project economics. Agencies are paid to build, not to maintain. Ongoing care is a hard sell once the launch budget is spent, so it gets dropped or underpriced.
Stack sprawl. Over a decade, a busy agency can end up running dozens of sites on different CMS versions, plugins and hosts. No one person holds the full map.
People move on. The developer who built it leaves. The account manager who sold it leaves. The site stays, with its version history in someone's old laptop.
Clients can't see it. A site on PHP 7.4 looks identical to one on PHP 8.4. Nothing prompts the conversation until something breaks.
AI is adding to the pile. Teams can now generate more sites, faster, across more tools. Without a shared foundation, that speed compounds the maintenance debt rather than reducing it.
What a responsible agency does
Agencies don't need to own every site forever. They do need to be clear about who does. Five steps would close most of the gap.
Keep a live register. Every site you've built or touched, its stack, its runtime version, its host and who owns it today.
Write the end date into the contract. State what happens after launch: who patches, who monitors, and what triggers a review.
Offer care as a product. Price maintenance as part of the build, not an awkward add-on six months later.
Tell clients when you see risk. Even if you have no contract, a short note on a disclosure like PHP2Shell protects them and your reputation.
Hand over properly. If a client leaves, give them the register entry, the credentials and a plain-English risk summary.
Designing responsibility in
The longer-term answer is to stop building on shonky foundations that make every agency its own fractional security team.
That is why we built Blutui as an Agency Web Ecosystem, from inside a working agency. Hosting, runtime, patching and delivery sit on one managed foundation that we maintain. Front-end teams keep control of their code and creative, through what we call createControl. Agencies keep the client relationship. The infrastructure burden moves to us.
When PHP2Shell was disclosed, our team checked and confirmed no Blutui agency site was affected. No agency had to audit a list of old builds that night. That is the shift I'd like to see across the industry: responsibility designed into the platform, not left to whoever is still around.
The question for Adland
We ask clients to trust us with their brand, their customers and their data. A website is so often where all three meet. If we put our name on it, we owe them a clear answer to one question: who is looking after this now?
PHP2Shell has been patched, for sites on current versions. The next disclosure is already on its way. The agencies that come out of it well will be the ones that decided, before it arrived, what their responsibility looks like after launch day.
Graeme Blake is Founder and CEO of Blutui, the Agency Web Ecosystem, and has spent more than 30 years in digital design and advertising.
More from Transform #24
-
Agency Life 2 min read
Switching dog food? Go slow. Switching platforms? Same rule.What the back of the bag knows
-
Agency Life 6 min read
SEO Didn't Die. Your Website Got a Promotion.Thanks to GEO Your Website Got a New Job, a Raise and the Corner Office.
-
4 min read
BIMA Unlocks the UK's Digital Front DoorBIMA asked one of its own members to rebuild the website of the UK digital industry. Subvert Studio did the research first, built on Blutui, and delivered in around a third of the planned time. Here's what agency leaders can take from it.
-
Agency Life 6 min read
You Can't Prompt Sunday NightYou Can't Prompt the Client: Why the Agency Is the Signal
-
Product 5 min read
Say It Like You Mean It, in Every LanguageA Blutui Insight on AI, human linguists and multilingual web production for agencies